Mythos found a login bypass in Rejetto HFS; attacks followed in a day
Horizon3 says Anthropic's Mythos chained a weak random-number generator into an admin login bypass in Rejetto HFS (CVE-2026-61500). The facts and limits.
In this article
Horizon3 says Anthropic’s Mythos model found a way to take over Rejetto HFS, a widely used file-sharing server, without a password, and that attackers started trying it about a day after the write-up. The bug is CVE-2026-61500. This article covers what the flaw is, how Horizon3 says Mythos found it, what has been reported about attacks, and what to do. We read Horizon3’s write-up, the HFS release notes and The Register’s report; we did not run the exploit or Mythos.
What is the Rejetto HFS flaw (CVE-2026-61500)?
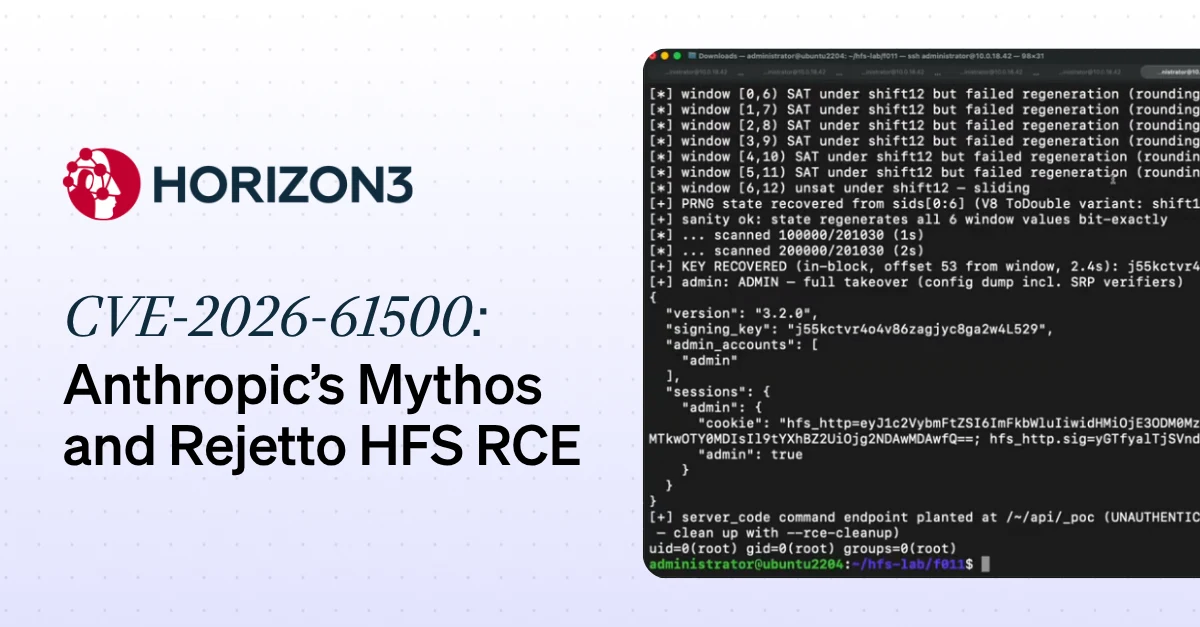
HFS 3.0.0 through 3.2.0 signs its session cookies with a key made at start-up by JavaScript’s Math.random(). That generator is not designed for secrets: in V8 it is the xorshift128+ algorithm, which Horizon3 calls non-cryptographic and invertible, meaning that enough consecutive outputs let you work out its internal state. HFS also leaks such outputs. According to Horizon3, the login endpoint puts a raw Math.random() value in the cookie it sends back to any visitor.
An attacker who can collect those values can reconstruct the generator, step it back to the moment the server started, recover the signing key and forge an administrator cookie. HFS’s admin API can then run custom JavaScript, which turns the login bypass into remote code execution. Horizon3’s exploit takes 12 samples from the leaking endpoint.
How did Mythos find it, according to Horizon3?
Horizon3 is part of Anthropic’s Project Glasswing, which gives vetted security teams access to Mythos. It says it runs the model inside a custom harness that starts specialized agents in parallel, each looking for one class of vulnerability. The agent focused on cryptographic weaknesses reportedly noticed the two facts together, a predictable key generator and a code path that leaks its output, and proposed using Microsoft’s open-source Z3 solver to recover the state. Horizon3 says this happened without follow-on prompting and that the model “exceeded what we thought was possible without significant harness engineering.”
That is Horizon3’s account of its own tool run, and Horizon3 is an Anthropic partner. The vulnerability class is well known, so the claim to weigh is how much of the chain the model assembled unaided, not whether such bugs exist.
Was it fixed before the attacks?
The timeline is easy to miss:
| Date | Event |
|---|---|
| July 13 | HFS 3.2.1 is released. Its notes say multiple vulnerabilities in all previous versions could allow administrative access, and thank Hanley “in collaboration with Claude and Anthropic Research.” |
| September 30 | Horizon3 publishes the write-up. |
| October 1 (evening) | VulnCheck’s Patrick Garrity sees exploitation, per The Register: one China-based address, against hosts in the US and Japan. |
| October 2 | Four more attempts, from two US addresses that appear to be proxies, per The Register. |
So the attacks targeted servers still running a version at least eleven weeks old, and the public write-up gave them a recipe. The Register also reports that 286 CVEs are now credited to Mythos and Project Glasswing and that only one earlier one had been exploited in the wild, figures we could not check independently. HFS has since moved on; its newest stable release at the time of writing is 3.3.4.
What should HFS users do?
- If you run Rejetto HFS, update to the latest release, at minimum 3.2.1, and check your admin accounts and server-side scripts for changes you did not make.
- If an HFS server is reachable from the internet and was on 3.2.0 or older, treat it as possibly compromised until you have checked.
- If you write code, do not derive secrets from
Math.random(), and do not expose raw random values to clients.
What to keep in mind
These are our observations:
- The patch was the news that mattered. The fix was public for weeks before the write-up; the write-up turned an unnoticed update into a race.
- The speed claim is narrow. “Exploited in a day” is VulnCheck’s observation as relayed by The Register, covering a few addresses, not proof of widespread compromise.
- Treat the model claims as claims. Horizon3 and Anthropic both gain from showing Mythos finding real bugs; the vulnerability and fix can be checked, the model’s share of the work is Horizon3’s word.
Editorial review: October 5, 2026 (AI). Prepared from Horizon3’s write-up (published September 30), the HFS 3.2.1 release notes and The Register’s report (October 3), all read the same day. We did not run the exploit, Mythos or VulnCheck’s data. The cover is Horizon3’s own card, reproduced with credit and a link to the source. “What to keep in mind” is ours.
Sources
Created with AI assistance.
Suggest a correction
Found an error or a missing source? Send a private suggestion to the editor. It will be reviewed and will not appear as a public comment. No name, email or account is needed.


Send us a message